Roles and Benefits for SBOM Across the Supply Chain
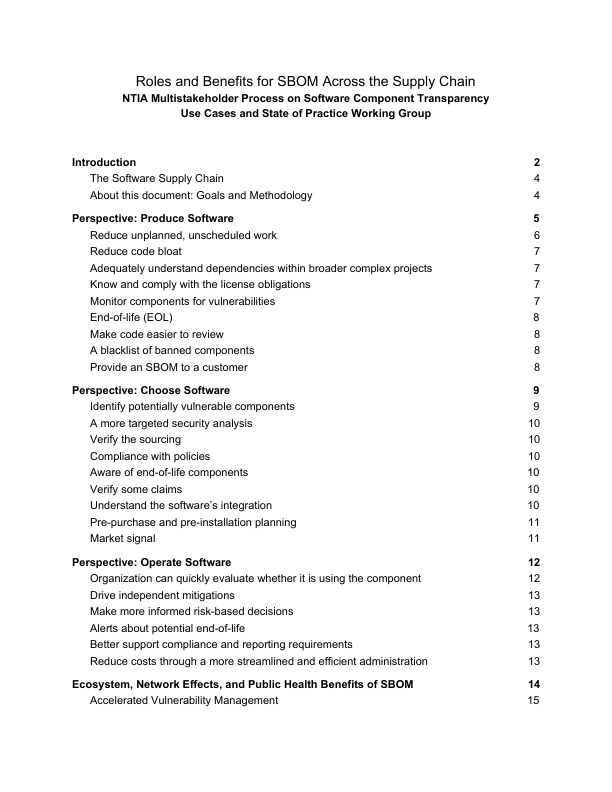
[[3. Resources/Readwise/Full Document Contents/Articles/Roles and Benefits for SBOM Across the Supply Chain|Full Document Contents]]
## Document Notes
---
tags:
- #SBOM
- #supplychain
- #softwaresecurity
- #transparency
- #opensource
- #vulnerabilitymanagement
- #compliance
- #riskmanagement
- #wordpress
- #devrel
Author: NTIA Use Cases Working Group
Source: NTIA publication (Website)
Reference: https://www.ntia.gov/files/ntia/publications/ntia_sbom_use_cases_roles_benefits-nov2019.pdf
date created: {{date:YYYY-MM-DD}} {{time:HH:mm}}
---
# Title: Roles and Benefits for SBOM Across the Supply Chain — Detailed Notes and Analysis
## Table of Contents
- [[#📝 Summary]]
- [[#📖 Main Content]]
- [[#🗒️ Notes]]
- [[#📖 References]]
- [[#🗣️ Paraphrase]]
- [[#📰 Newsletter]]
- [[#✅ Action Items]]
- [[#🧪 Hypotheses]]
- [[#📊 Methodology]]
- [[#❓ Questions]]
- [[#🔮 Future Research]]
- [[#💡 Implications]]
- [[#🧠 Learning Styles Assessment]]
- [[#📊 Accessibility Assessment]]
- [[#🌍 DEIB Assessment]]
- [[#✅ Logical validity]]
- [[#🔍 DARVO Analysis]]
- [[#🔍 SEO Evaluation]]
- [[#🎯 Conclusion]]
### References
- NTIA: “Roles and Benefits for SBOM Across the Supply Chain” (Nov 2019)
- Related: NTIA Software Transparency initiative
- BSIMM v9, NIST SSDF (2019 draft), OWASP Component Analysis, SAFECode, MITRE “Deliver Uncompromised”
## 📝 Summary
The document argues that Software Bills of Materials (SBOMs) are foundational for software supply chain transparency and risk management. It organizes benefits across three roles:
- Produce software: reduce unplanned work, code bloat, and security risk; understand dependencies; manage licensing; monitor vulnerabilities and EOL.
- Choose software: evaluate vulnerabilities, verify sourcing, enforce policy compliance, validate supplier claims, plan pre-installation mitigations, and use SBOMs as a market signal.
- Operate software: rapidly evaluate exposure, drive independent mitigations, support risk-based decisions, anticipate EOL, meet reporting/compliance needs, and reduce operational costs.
It also highlights ecosystem-level “public health” effects: accelerated vulnerability management, amplified herd immunity through shared improvements, selection pressure for better suppliers, resilience when suppliers disappear, and cumulative value. Appendices discuss SBOM depth (beyond 1-hop) and assurance elements (provenance, pedigree, integrity).
## 📖 Main Content
The paper frames software development as a supply chain in which components are assembled across multiple tiers. Unlike physical supply chains, software dependencies are numerous, weakly coupled commercially, and change frequently, increasing systemic risk. SBOMs provide a structured inventory of components (and ideally their versions, origins, and hashes) to enable:
- Faster and targeted vulnerability response when new CVEs emerge.
- Strategic dependency management and standardization to reduce attack surface and operational toil.
- Policy-driven licensing and sourcing controls.
- Measurable supplier performance (e.g., mean time to remediate).
- Ecosystem-wide improvements via network effects.
Key operational insights:
- SBOMs serve as a “roadmap for the defender,” enabling quick exposure checks and compensating controls.
- Depth matters: 1-hop SBOMs can miss deeply nested risky components (e.g., Urgent/11 where issues traced to Interpeak IPnet under VxWorks).
- Assurance features (provenance, pedigree, integrity) strengthen SBOM reliability under active adversarial threats.
Connections:
- Aligns with BSIMM, NIST SSDF (recommends creating and maintaining SBOMs), OWASP guidance to require SBOMs in procurement, SAFECode practices, and MITRE supply chain recommendations.
- Applies across sectors including healthcare, industrial control, and finance, where patch timelines and regulatory expectations heighten the need.
## 🗒️ Notes
- Produce software
- Reduce unplanned work by quickly pinpointing affected components after a vulnerability disclosure.
- Reduce code bloat via standardizing component choices; one fix propagates across products.
- Understand complex dependency graphs; plan maintenance and team expertise.
- License compliance automation; policy enforcement on allowed/denied licenses.
- Monitor vulnerabilities and EOL proactively; plan contingencies when projects end support.
- Ease reviews, simplify builds, and anticipate change impact.
- Use blacklists/whitelists informed by operational metrics and SBOM feedback loops.
- Provide SBOMs to customers as a trust and competitive differentiator.
- Choose software
- Identify vulnerable or orphaned components pre-purchase.
- Targeted security analysis focusing on high-risk libraries (e.g., crypto).
- Verify sourcing using signatures/hashes to detect counterfeit/backdoored parts.
- Enforce regulatory and internal sourcing policies.
- Detect EOL components likely to lack future fixes.
- Validate supplier claims and development hygiene.
- Plan segmentation and compensating controls pre-installation.
- Market signal rewarding security-mature suppliers and faster MTTx.
- Operate software
- Rapid exposure evaluation to “Am I affected and where?”
- Independent mitigations while awaiting vendor patches (isolation, procedural controls, heightened monitoring).
- Risk-prioritized response using SBOM as a defender’s roadmap.
- Early alerts for impending EOL and ripple effect planning.
- Support compliance/reporting (e.g., post-market surveillance).
- Reduce operational costs by eliminating unnecessary supplier outreach when unaffected.
- Ecosystem/public health
- Accelerated remediation across tiers; parallelize awareness and action.
- Herd immunity via upstream avoidance of vulnerable versions.
- Selection for better suppliers through transparency and measurable performance.
- Resilience to supplier extinction; self-assessment without upstream notifications.
- Cumulative value compounds as adoption expands.
- Depth vs effectiveness
- 1-hop visibility can be <10% of actual dependencies; multi-hop recursion is crucial.
- Urgent/11 shows necessity of tracing dependencies-of-dependencies.
- Assurance/Confidence
- Provenance: chain of custody, authors, and acquisition sources.
- Pedigree: how components were built/assembled; build options (e.g., ASLR).
- Integrity: cryptographic protections for SBOM tamper-evidence.
## 📖 References
- NIST SSDF (recommends maintaining SBOMs): https://csrc.nist.gov/publications/detail/white-paper/2019/06/11/mitigating-risk-of-software-vulnerabilities-with-ssdf/draft
- MITRE “Deliver Uncompromised” (SBOM for supply chain integrity): https://www.mitre.org/publications/technical-papers/deliver-uncompromised-a-strategy-for-supply-chain-security
- OWASP Component Analysis (procurement with SBOM): https://owasp.org/www-project-component-analysis/
- SAFECode on third-party components: https://safecode.org/resources/
- BSIMM: https://www.bsimm.com/
## 🗣️ Paraphrase
- Original: “The supply chain is a simple model of how products are made, but it doesn’t answer every possible question. What happens when something goes wrong with a link in the chain?”
- Paraphrase: The supply chain model explains production flow, but it falls short when a particular link fails—leaving open how to diagnose and respond to failures across tiers.
- Original: “In the world of software, the links between dependencies are weaker... And unlike most physical parts, software components change constantly.”
- Paraphrase: Software dependencies are loosely bound and often lack direct commercial ties, and they evolve continuously—making their risks dynamic and harder to govern than physical components.
## 📰 Newsletter
Title: Building Safer Stacks: SBOMs, Learning Paths, and What’s New in WP
Hey devs! This week we’re doubling down on learning and shipping smarter:
- Learn web development: Start with a friendly “HTML/CSS → JS → WordPress/PHP” path. Pair docs with practice: build a theme block by block, wire it
> [!note]+ Document Notes
> tags:
> - #SBOM
> - #supplychain
> - #softwaresecurity
> - #transparency
> - #opensource
> - #vulnerabilitymanagement
> - #compliance
> - #riskmanagement
> - #wordpress
> - #devrel
>
> Author: NTIA Use Cases Working Group
> Source: NTIA publication (Website)
> Reference: https://www.ntia.gov/files/ntia/publications/ntia_sbom_use_cases_roles_benefits-nov2019.pdf
> date created: {{date:YYYY-MM-DD}} {{time:HH:mm}}
>
> # Title: Roles and Benefits for SBOM Across the Supply Chain — Detailed Notes and Analysis
>
<!-- deep-read:sections start -->
## Table of Contents
- [📝 Summary](#-summary)
- [📖 Main Content](#-main-content)
- [🗒️ Notes](#-️-notes)
- [📖 References](#-references)
- [🗣️ Paraphrase](#-paraphrase)
- [📰 Newsletter](#-newsletter)
- [✅ Action Items](#-action-items)
- [🧪 Hypotheses](#-hypotheses)
- [📊 Methodology](#-methodology)
- [❓ Questions](#-questions)
- [🔮 Future Research](#-future-research)
- [💡 Implications](#-implications)
- [🧠 Learning Styles Assessment](#-learning-styles-assessment)
- [📊 Accessibility Assessment](#-accessibility-assessment)
- [🌍 DEIB Assessment](#-deib-diversity-equity-inclusion-and-belonging-assessment)
- [✅ Logical validity](#-logical-validity)
- [🔍 DARVO Analysis](#-darvo-analysis-prompt)
- [🔍 SEO Evaluation](#-seo-evaluation)
- [🎯 Conclusion](#-conclusion)
### References
- NTIA: “Roles and Benefits for SBOM Across the Supply Chain” (Nov 2019)
- Related: NTIA Software Transparency initiative
- BSIMM v9, NIST SSDF (2019 draft), OWASP Component Analysis, SAFECode, MITRE “Deliver Uncompromised”
## 📝 Summary
The document argues that Software Bills of Materials (SBOMs) are foundational for software supply chain transparency and risk management. It organizes benefits across three roles:
- Produce software: reduce unplanned work, code bloat, and security risk; understand dependencies; manage licensing; monitor vulnerabilities and EOL.
- Choose software: evaluate vulnerabilities, verify sourcing, enforce policy compliance, validate supplier claims, plan pre-installation mitigations, and use SBOMs as a market signal.
- Operate software: rapidly evaluate exposure, drive independent mitigations, support risk-based decisions, anticipate EOL, meet reporting/compliance needs, and reduce operational costs.
It also highlights ecosystem-level “public health” effects: accelerated vulnerability management, amplified herd immunity through shared improvements, selection pressure for better suppliers, resilience when suppliers disappear, and cumulative value. Appendices discuss SBOM depth (beyond 1-hop) and assurance elements (provenance, pedigree, integrity).
## 📖 Main Content
The paper frames software development as a supply chain in which components are assembled across multiple tiers. Unlike physical supply chains, software dependencies are numerous, weakly coupled commercially, and change frequently, increasing systemic risk. SBOMs provide a structured inventory of components (and ideally their versions, origins, and hashes) to enable:
- Faster and targeted vulnerability response when new CVEs emerge.
- Strategic dependency management and standardization to reduce attack surface and operational toil.
- Policy-driven licensing and sourcing controls.
- Measurable supplier performance (e.g., mean time to remediate).
- Ecosystem-wide improvements via network effects.
Key operational insights:
- SBOMs serve as a “roadmap for the defender,” enabling quick exposure checks and compensating controls.
- Depth matters: 1-hop SBOMs can miss deeply nested risky components (e.g., Urgent/11 where issues traced to Interpeak IPnet under VxWorks).
- Assurance features (provenance, pedigree, integrity) strengthen SBOM reliability under active adversarial threats.
Connections:
- Aligns with BSIMM, NIST SSDF (recommends creating and maintaining SBOMs), OWASP guidance to require SBOMs in procurement, SAFECode practices, and MITRE supply chain recommendations.
- Applies across sectors including healthcare, industrial control, and finance, where patch timelines and regulatory expectations heighten the need.
## 🗒️ Notes
- Produce software
- Reduce unplanned work by quickly pinpointing affected components after a vulnerability disclosure.
- Reduce code bloat via standardizing component choices; one fix propagates across products.
- Understand complex dependency graphs; plan maintenance and team expertise.
- License compliance automation; policy enforcement on allowed/denied licenses.
- Monitor vulnerabilities and EOL proactively; plan contingencies when projects end support.
- Ease reviews, simplify builds, and anticipate change impact.
- Use blacklists/whitelists informed by operational metrics and SBOM feedback loops.
- Provide SBOMs to customers as a trust and competitive differentiator.
- Choose software
- Identify vulnerable or orphaned components pre-purchase.
- Targeted security analysis focusing on high-risk libraries (e.g., crypto).
- Verify sourcing using signatures/hashes to detect counterfeit/backdoored parts.
- Enforce regulatory and internal sourcing policies.
- Detect EOL components likely to lack future fixes.
- Validate supplier claims and development hygiene.
- Plan segmentation and compensating controls pre-installation.
- Market signal rewarding security-mature suppliers and faster MTTx.
- Operate software
- Rapid exposure evaluation to “Am I affected and where?”
- Independent mitigations while awaiting vendor patches (isolation, procedural controls, heightened monitoring).
- Risk-prioritized response using SBOM as a defender’s roadmap.
- Early alerts for impending EOL and ripple effect planning.
- Support compliance/reporting (e.g., post-market surveillance).
- Reduce operational costs by eliminating unnecessary supplier outreach when unaffected.
- Ecosystem/public health
- Accelerated remediation across tiers; parallelize awareness and action.
- Herd immunity via upstream avoidance of vulnerable versions.
- Selection for better suppliers through transparency and measurable performance.
- Resilience to supplier extinction; self-assessment without upstream notifications.
- Cumulative value compounds as adoption expands.
- Depth vs effectiveness
- 1-hop visibility can be <10% of actual dependencies; multi-hop recursion is crucial.
- Urgent/11 shows necessity of tracing dependencies-of-dependencies.
- Assurance/Confidence
- Provenance: chain of custody, authors, and acquisition sources.
- Pedigree: how components were built/assembled; build options (e.g., ASLR).
- Integrity: cryptographic protections for SBOM tamper-evidence.
## 📖 References
- NIST SSDF (recommends maintaining SBOMs): https://csrc.nist.gov/publications/detail/white-paper/2019/06/11/mitigating-risk-of-software-vulnerabilities-with-ssdf/draft
- MITRE “Deliver Uncompromised” (SBOM for supply chain integrity): https://www.mitre.org/publications/technical-papers/deliver-uncompromised-a-strategy-for-supply-chain-security
- OWASP Component Analysis (procurement with SBOM): https://owasp.org/www-project-component-analysis/
- SAFECode on third-party components: https://safecode.org/resources/
- BSIMM: https://www.bsimm.com/
## 🗣️ Paraphrase
- Original: “The supply chain is a simple model of how products are made, but it doesn’t answer every possible question. What happens when something goes wrong with a link in the chain?”
- Paraphrase: The supply chain model explains production flow, but it falls short when a particular link fails—leaving open how to diagnose and respond to failures across tiers.
- Original: “In the world of software, the links between dependencies are weaker... And unlike most physical parts, software components change constantly.”
- Paraphrase: Software dependencies are loosely bound and often lack direct commercial ties, and they evolve continuously—making their risks dynamic and harder to govern than physical components.
## 📰 Newsletter
Title: Building Safer Stacks: SBOMs, Learning Paths, and What’s New in WP
Hey devs! This week we’re doubling down on learning and shipping smarter:
- Learn web development: Start with a friendly “HTML/CSS → JS → WordPress/PHP” path. Pair docs with practice: build a theme block by block, wire it to a simple plugin, and version it in Git. Daily reps > marathon weekends.
- Recent updates: WordPress core performance improvements continue, and the block editor API sees incremental polish. Keep an eye on core dev notes and Make blogs for breaking changes in block patterns and theme.json.
- Community highlights: Props to contributors onboarding new maintainers in Five for the Future—your mentorship is multiplying impact across the ecosystem.
- New plugins to watch: Lint your blocks, audit enqueued assets, and test your site health in CI. Bonus points for plugins that export an SBOM of your site’s dependencies to speed up vulnerability audits.
- Why SBOMs matter: Treat your site like a product: inventory your npm/PHP libraries, pin versions, and monitor advisories. Faster triage, fewer surprises.
Helpful starting points:
- WordPress Developer Resources: https://developer.wordpress.org/
- Node Security advisories: https://github.com/advisories
- PHP Security advisories: https://packagist.org/explore/security-advisories
Build, learn, share—and remember: ship often, ship safely!
## ✅ Action Items
Prompt you can reuse for alignment with your Developer Advocate and OSPO trajectory:
“Analyze how this article advances:
- Open-source advocacy: Identify where SBOMs promote transparency, community trust, and sustainability funding paths (e.g., selecting suppliers with better MTTx, rewarding secure OSS projects).
- Contributor engagement: Extract ways SBOMs make onboarding easier (clear dependency maps, license clarity), and propose contributor-friendly documentation and tooling.
- Education: Design workshops/demos for WordPress and PHP/JS ecosystems on SBOM generation (e.g., CycloneDX, SPDX), vulnerability triage, and policy enforcement via CI/CD.
- OSPO objectives: Map SBOM policy to procurement, risk/compliance reporting, and internal standards (e.g., minimum SBOM depth, provenance/integrity requirements).
- WordPress ecosystem: Recommend patterns for plugin/theme devs (dependency standardization, EOL alerts), and governance proposals for including SBOMs in plugin submissions.
- Transparency & inclusivity: Ensure accessible docs, clear language for non-native speakers, and equitable processes for smaller maintainers to comply without undue burden.
Summarize concrete next steps, KPIs (e.g., time-to-detect, time-to-remediate, SBOM coverage), and a communication plan for internal stakeholders and the community.”
## 🧪 Hypotheses
- H1: Projects that adopt multi-hop SBOMs achieve significantly lower mean time to remediate CVEs than those with 1-hop or no SBOM.
- H2: Publishing SBOMs at procurement time reduces the incidence of post-install vulnerability surprises in enterprise environments.
- H3: SBOM transparency shifts market share toward suppliers with faster MTTx over 12–24 months.
- H4: WordPress plugins/themes that publish SBOMs experience higher trust and adoption in enterprise contexts.
- H5: Including SBOM integrity (signatures) reduces successful supply-chain tampering incidents.
### 📊 Methodology
- Data sources: CVE/NVD feeds, GitHub advisories, vendor advisories, package registries (npm, Packagist), enterprise ticket metrics, WP plugin directory metadata.
- Designs:
- Quasi-experimental cohort study comparing SBOM-adopting vs. non-adopting projects (matched by size/domain).
- Time-series analysis of MTTx before/after SBOM rollout.
- Procurement A/B test: RFPs requiring SBOM vs. not; measure downstream incidents.
- WordPress field study: pilot SBOMs in selected top plugins/themes; track installs and enterprise adoption signals.
- Analysis: Survival analysis (remediation time), regression with controls (project size, complexity), difference-in-differences for policy changes, hazard models for vulnerability closure.
### ❓ Questions
- What minimum SBOM depth balances effectiveness and effort for typical web stacks?
- How should organizations validate SBOM authenticity at scale?
- What incentives most effectively drive suppliers to improve MTTx?
- How can the WP plugin ecosystem standardize SBOM submission without excluding small maintainers?
### 🔮 Future Research
- Automated recursive SBOM generation across polyglot builds (JS/PHP/CSS assets).
- Standard EOL signaling in SBOM formats.
- Integrating SBOMs with SBVR/GRC tools for policy-as-code.
- Community funding models rewarding secure maintenance informed by SBOM-derived metrics.
### 💡 Implications
- Policy: Governments and large buyers can mandate SBOMs to lift baseline security and measurability.
- Practice: CI/CD-integrated SBOMs shorten detection and remediation lifecycles.
- Knowledge: Establishes common metrics for supplier performance and risk transparency.
- Community: Encourages sustainable support for well-maintained OSS libraries.
### 🧠 Learning Styles Assessment
- Readability: General professional/industry level; likely Grade 12–14 (advanced, but approachable for practitioners).
- Visual (spatial)
- Present: Conceptual figures (remediation timelines, depth diagrams) mentioned.
- Improve: Add dependency graphs, SBOM schema examples, end-to-end supply chain diagrams.
- Aural (auditory)
- Present: None.
- Improve: Provide audio summary or recorded webinar walkthrough.
- Verbal (linguistic)
- Present: Clear definitions, structured sections, concrete examples.
- Improve: Add more narratives/case studies and glossaries.
- Physical (kinesthetic)
- Present: None.
- Improve: Hands-on labs: generate SBOMs, simulate CVE triage, enforce license policy in CI.
- Logical (mathematical)
- Present: Causal chains, process logic, metrics discussion (MttR).
- Improve: Provide formulas/KPIs, sample dashboards, and decision trees.
- Social (interpersonal)
- Present: Multistakeholder framing.
- Improve: Discussion prompts, cohort exercises, community forums.
- Solitary (intrapersonal)
- Present: Reflective sections on methodology and roles.
- Improve: Self-assessment checklists and journaling prompts (current SBOM maturity).
- Naturalistic
- Present: “Public health/herd immunity” analogy.
- Improve: Sustainability framing (resource waste reduction via standardization).
### 📊 Accessibility Assessment
- Screen reader compatibility: As a PDF, semantics depend on tagging; may be limited.
- Improve: Provide semantic HTML version, tag headings/lists, alt-text for figures.
- Keyboard navigation: PDF may be less optimal.
- Improve: Offer web-native article with skip links and proper landmarks.
- Contrast/readability: Typical PDF contrast likely OK; font scalability unknown.
- Improve: High-contrast theme in web version; ensure text reflow without content loss.
- Text resizing: PDFs often don’t reflow well.
- Improve: Responsive HTML with scalable fonts and media queries; avoid image-only text.
### 🌍 DEIB (Diversity, Equity, Inclusion, and Belonging) Assessment
- Cultural relevance: Primarily US-centric references (NTIA, FDA, NIST).
- Improve: Include global standards (ISO/IEC, ENISA) and diverse sector case studies.
- Inclusive language: Generally neutral and technical.
- Improve: Define acronyms, reduce jargon, add plain-language summaries.
- Neurodiversity support: Long sections with dense text.
- Improve: Chunk content with headings, bullets, summaries, and visuals; provide TL;DRs.
- Representation: Limited explicit representation examples.
- Improve: Feature cases from varied org sizes, regions, and maintainer demographics.
- Psychological safety: Neutral tone.
- Improve: Add guidance on constructive disclosure, non-punitive postmortems, and respectful collaboration norms.
### ✅ Logical validity
- Tone: Professional, instructive, consensus-building.
- Strong reasoning
- Causal reasoning: “SBOMs collapse disclosure delays across tiers → faster remediation” strengthens the public-health analogy; could be enhanced by quantified case studies.
- Inductive reasoning: Observations from interviews and industry practices generalize to proposed benefits; would be stronger with broader datasets.
- Consistent analogies: “Herd immunity” frames network effects to show how upstream fixes protect downstream; clear and apt.
- Appeal to evidence: Cites BSIMM, NIST SSDF, MITRE; bolsters credibility; could add comparative metrics.
- Logical flow: Role-based structure (produce, choose, operate) → ecosystem effects → appendices; coherent progression.
- Ethical reasoning: Emphasizes transparency, safety, and continuous improvement; aligns with public interest.
- Potential weaknesses/fallacies
- Hasty generalization risk: Claims of market selection for better suppliers could overgeneralize without longitudinal evidence; improve with procurement datasets.
- Post hoc/correlation vs causation: Faster remediation may correlate with mature orgs that also adopt SBOMs; control for maturity in studies.
- Appeal to authority: Heavy reliance on standards bodies; complement with empirical benchmarks and cross-sector data.
🔍 Recommendations to improve rigor:
- Provide controlled before/after metrics for SBOM adoption.
- Publish benchmarks for MTTx across suppliers with/without SBOM requirements.
- Expand multi-region and multi-industry evidence.
🔍 DARVO Analysis Prompt
- Deny: No evidence of denial tactics; the document acknowledges gaps (e.g., need for deeper SBOM, assurance features).
- Attack: No personal attacks; discourse remains constructive and technical.
- Reverse Victim and Offender: None; the paper does not cast accusers/suppliers as victims or offenders.
- Notes: Tone is collaborative and solution-focused, free of manipulative rhetoric or adversarial framing. No DARVO indicators present.
### 🔍 SEO Evaluation
Note: As a PDF on a government site, classic web SEO factors are constrained.
- Keywords
- Present: “SBOM,” “software supply chain,” “vulnerability management,” “end-of-life.”
- Improve: Ensure these appear in title/first paragraph of an HTML companion page; add long-tail variants (e.g., “multi-hop SBOM,” “SBOM provenance”).
- Meta description
- Likely absent for PDF.
- Improve: Create an HTML landing page with a 150–160 character meta description including “SBOM” and “software supply chain transparency.”
- Title tag
- Good clarity; ensure 50–60 characters on HTML page: “SBOM Roles and Benefits Across the Supply Chain.”
- Headers (H1–H3)
- PDF headings exist; mirror structure in HTML with proper H-tags and keywords.
- Content length/value
- Sufficient depth; clearly valuable.
- Internal/external links
- Improve: On HTML page, link to related NTIA SBOM resources and authoritative external references (NIST, MITRE, OWASP).
- URL structure
- PDF URL is fine but long; add concise HTML URL (e.g., /sbom-roles-benefits).
- Image optimization
- Add alt text and descriptive filenames for figures on the HTML version; optimize sizes.
- Mobile optimization
- Provide responsive HTML; optimize page speed with minimal render-blocking resources.
- User engagement
- Add CTAs: download SBOM templates, view tooling, join working groups.
- Schema markup
- Use Article schema; consider FAQ schema for common SBOM questions.
- Social sharing
- Add Open Graph/Twitter Card tags with a clear summary and preview image.
## 🎯 Conclusion
SBOMs provide a practical, scalable way to increase transparency and resilience across the software supply chain. They deliver immediate benefits to producers (dependency clarity, licensing, vulnerability monitoring), choosers (procurement assurance, risk planning), and operators (faster exposure checks, mitigations, compliance), while compounding ecosystem gains through accelerated remediation, herd immunity, and supplier selection pressure. Multi-hop depth and assurance attributes (provenance, pedigree, integrity) are essential for effectiveness and adversarial contexts. For WordPress and broader open-source communities, SBOM adoption aligns with transparency, education, and sustainable security—creating measurable pathways toward better practices, safer deployments, and stronger trust.
<!-- deep-read:sections end -->
## Highlights
- Roles and Benefits for SBOM Across the Supply Chain ([View Highlight](https://read.readwise.io/read/01h4kqwb1vg1axpx6cnm4ha4k0))