Is WordPress.org GDPR Compliant?

## Metadata
- Author: [[Terence Eden’s Blog]]
- Full Title: Is WordPress.org GDPR Compliant?
- Category: #articles
- Document Note: ---
tags: [#WordPress, #GDPR, #Compliance, #Automattic, #Privacy]
Author: Terence Eden
Source: Personal Blog
Reference: [Is WordPress.org GDPR Compliant?](https://shkspr.mobi/blog/2024/12/is-wordpress-org-gdpr-compliant/?__readwiseLocation=)
date created: 2024-12-11 17:15
---
# Title: Is WordPress.org GDPR Compliant?
## Table of Contents:
- [📝 Summary](#-summary)
- [📖 Main Content](#-main-content)
- [🗒️ Notes](#-notes)
- [📖 References](#-references)
- [🗣️ Paraphrase](#-paraphrase)
- [📰 Newsletter](#-newsletter)
- [✅ Action Items](#-action-items)
- [🧪 Hypotheses](#-hypotheses)
- [📊 Methodology](#-methodology)
- [❓ Questions](#-questions)
- [🔮 Future Research](#-future-research)
- [💡 Implications](#-implications)
- [🧠 Learning Styles Assessment](#-learning-styles-assessment)
- [📊 Accessibility Assessment](#-accessibility-assessment)
- [🌍 DEIB Assessment](#-deib-assessment)
- [✅ Logical Validity](#-logical-validity)
- [🔍 DARVO Analysis](#-darvo-analysis)
- [🔍 SEO Evaluation](#-seo-evaluation)
- [🎯 Conclusion](#-conclusion)
## 📝 Summary:
This blog post questions WordPress.org's compliance with GDPR (General Data Protection Regulation). The author recounts their experience with a GDPR data access request and reveals concerning practices regarding privacy and data handling. The post critiques WordPress.org’s lack of a proper Data Protection Officer (DPO), GDPR policy, and accountability for processing user data. It argues for better transparency and governance in WordPress's operations, particularly in its Slack communications.
## 📖 Main Content:
The blog outlines significant issues related to WordPress.org’s data privacy practices:
1. WordPress.org claims it is privately owned by Matt Mullenweg and not bound by GDPR as it is not a registered entity.
2. A Slack account ban prompted the author to request data under GDPR, revealing poor handling and misunderstandings of GDPR obligations.
3. Volunteers manage privacy queries but lack formal training or legal accountability.
4. Slack’s ownership structure conflicts with its data controller obligations under GDPR, leading to potential violations.
### 🗒️ Notes
- **GDPR Compliance Issues**:
- WordPress.org asserts it is not a GDPR-compliant entity.
- Lack of formalized DPO role, relying instead on volunteer efforts.
- Slack communications suggest insufficient understanding of data processing obligations.
- **Data Access Request**:
- Initial request denied; later clarified no records existed beyond the ban.
- Responses from WordPress.org reveal fundamental GDPR misunderstandings.
- **Ownership Concerns**:
- WordPress.org asserts it is "privately owned," limiting accountability.
- Conflicts with Slack’s requirement for organizational compliance with GDPR.
- **Implications**:
- Raises questions about the transparency and governance of WordPress.org.
- Highlights broader issues in managing privacy for open-source projects.
## 📖 References:
- Eden, T. (2024). *Is WordPress.org GDPR Compliant?* Retrieved from [link](https://shkspr.mobi/blog/2024/12/is-wordpress-org-gdpr-compliant/?__readwiseLocation=)
## 🗣️ Paraphrase:
1. WordPress.org claims GDPR exemptions due to its status as a privately owned entity, undermining its accountability for user data.
2. The blog critiques WordPress.org’s Slack management, highlighting that its administration conflicts with GDPR’s data controller requirements.
## 📰 Newsletter:
🌐 **GDPR Compliance in Question!**
A recent post scrutinizes WordPress.org’s handling of GDPR obligations, revealing gaps in its data privacy practices. The author highlights issues ranging from unclear data ownership to poorly managed user privacy requests. This raises critical questions about governance and accountability within open-source communities. [Read more here.](https://shkspr.mobi/blog/2024/12/is-wordpress-org-gdpr-compliant/?__readwiseLocation=)
## ✅ Action Items:
- Explore strategies for improving GDPR compliance in open-source projects.
- Advocate for transparent governance frameworks that align with privacy laws.
- Develop resources to train open-source volunteers on data protection practices.
## 🧪 Hypotheses:
- Clearer governance structures enhance privacy compliance in open-source communities.
- Volunteer-driven privacy roles increase risks of non-compliance.
### 📊 Methodology:
- **Data Sources**: Privacy policies, GDPR case studies, user surveys.
- **Research Design**: Comparative analysis of compliant and non-compliant organizations.
- **Analysis Techniques**:
- Document Tags: [[gdpr]] [[lawsuit]] [[matt mullenweg]] [[wordpress]] [[wordpress.org]] [[wpdrama]] [[wp engine]]
- Summary: A few weeks ago, I got a chance to speak truth to power. I used my WordPress.org account to sign in to the official WordPress.org Slack where the various WordPress dramas were being discussed. After a brief chat about the latest shenanigans, I publicly replied to the CEO: Here's a link to the full exchange There was no reply forthcoming - although, as you can see, my message gathered a fair few positive reactions. As was inevitable, the next morning I found myself locked out of the Slack.…
- URL: https://shkspr.mobi/blog/2024/12/is-wordpress-org-gdpr-compliant/
A few weeks ago, I got a chance to speak truth to power. I used my WordPress.org account to sign in to the [official WordPress.org Slack](https://make.wordpress.org/chat/) where the various [WordPress dramas](https://mullenweg.wtf/) were being discussed.
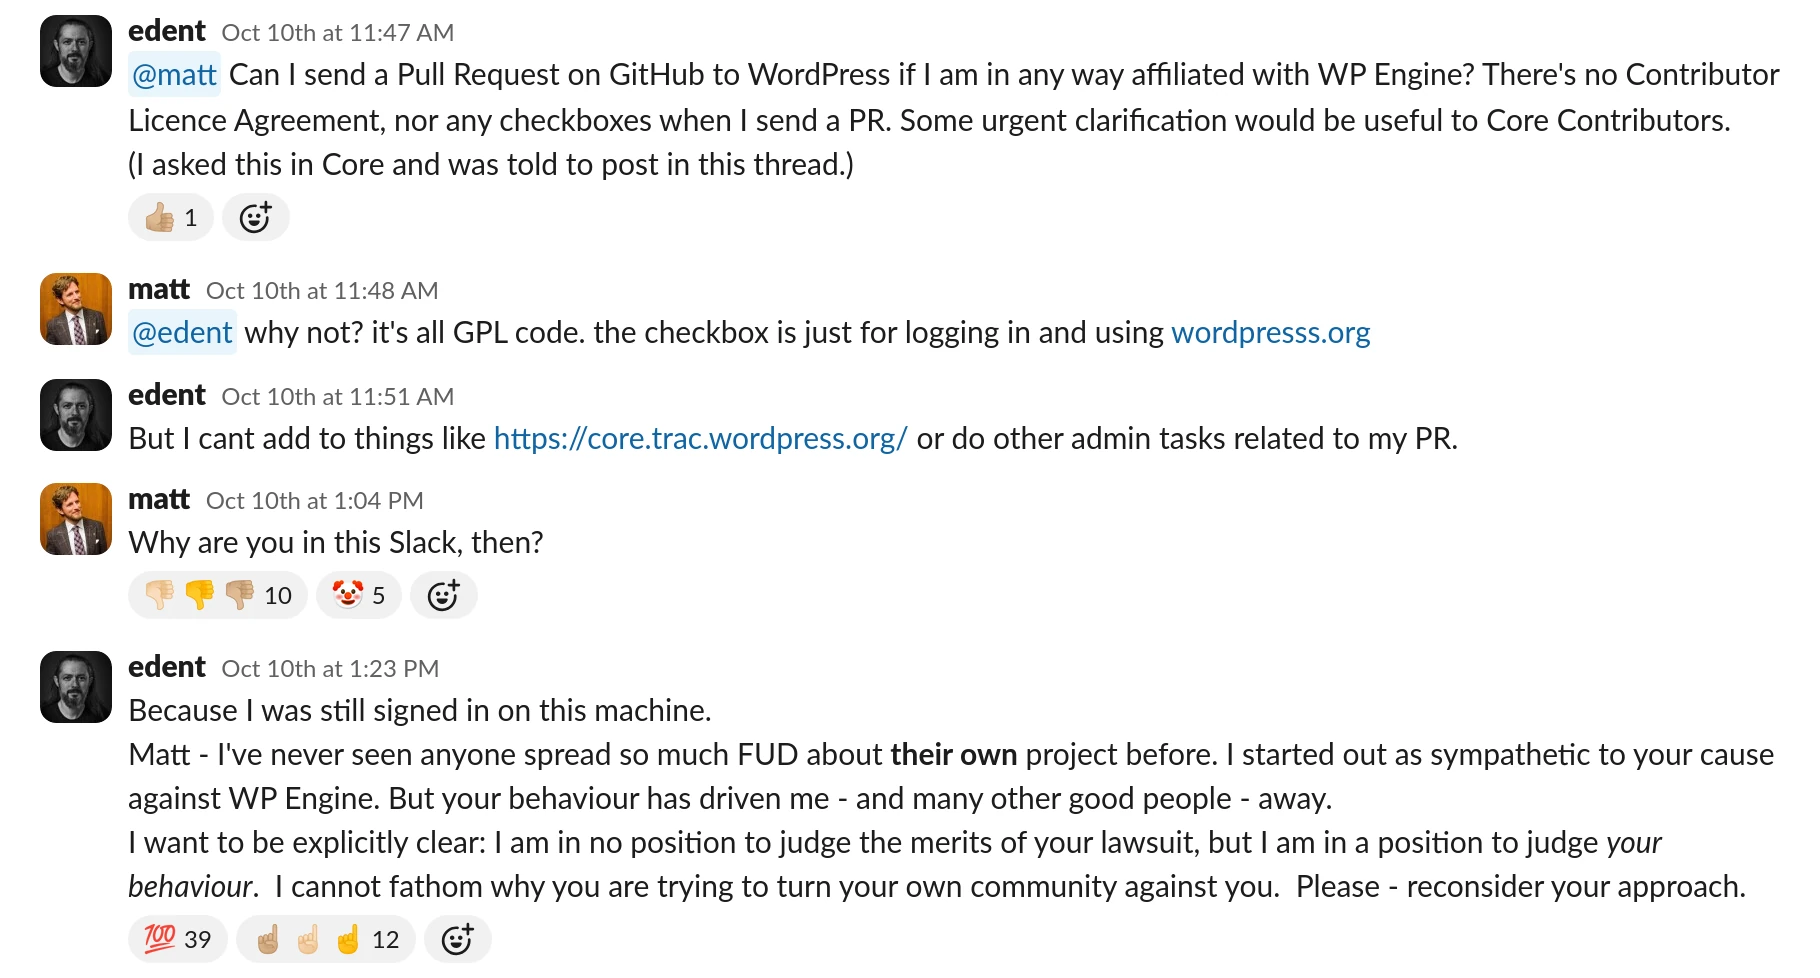
After a brief chat about the latest shenanigans, I publicly replied to the CEO:
[](https://wordpress.slack.com/archives/C02QB8GMM/p1728563007042769?thread_ts=1728463928.352389&cid=C02QB8GMM)
Here's [a link to the full exchange](https://wordpress.slack.com/archives/C02QB8GMM/p1728563007042769?thread_ts=1728463928.352389&cid=C02QB8GMM)
There was no reply forthcoming - although, as you can see, my message gathered a fair few positive reactions. [As was inevitable](https://mastodon.social/@Edent/113283116807769292), the next morning I found myself locked out of the Slack. I had been permabanned.
Then things got *weird*.
Someone claiming to be an employee of Automattic sent me a message saying that Matt had personally told people to ban me. I didn't know if they were telling the truth, but the GDPR gives me the right to see the data a company holds about me. That includes *messages* about me stored on their internal systems.
The [WordPress.org Privacy Policy](https://wordpress.org/about/privacy/) gave me an email address for their Data Protection Officer (DPO). So I sent a friendly(ish) message. After a little back-and-forth to clarify which data I wanted, I received this truly bizarre reply.
> We are in receipt of your request, which you claim is justified by GDPR. Accordingly, we are processing your request pursuant to section 15(3) of GDPR, which requires us to provide personal information about the person that we are processing. You refer to messages sent about you on internal systems. To the extent those are outside the scope of GDPR, they are not covered by your request.
>
>
This betrays a fundamental misunderstanding of GDPR. There is not, as far as I know, an exemption for records held on internal systems. There are [a list of GDPR exemptions](https://ico.org.uk/for-organisations/uk-gdpr-guidance-and-resources/exemptions/a-guide-to-the-data-protection-exemptions/) - but they mostly relate to things like the detection of crime, academic and journalistic exemptions, health and social work data, etc.
Of course, there is an [exemption for the purposes of self-incrimination](https://www.legislation.gov.uk/ukpga/2018/12/schedule/2/paragraph/20/enacted). Perhaps that's what they're relying upon?
I replied with a (not so-friendly) email pointing out that I was entitled to a copy of any messages *because* they contain my personal data. I also pointed out that my request was neither manifestly unfounded nor manifestly excessive (another common get-out clause).
A week later, they replied:
> I’ve followed up looking for any related records, and can confirm no records which use your likeness exist, other than the following: `edent was deactivated by <<REDACTEDUSER>>` No records exist where this was discussed beforehand.
>
>
I take this to mean that either Matt personally swung the ban-hammer, without discussing it with anyone else, or that a flunky wanted to protect their master's ego and took unilateral action.
They only provided me with messages from Slack that I had sent. They didn't provide any of the messages that mentioned me.
I pushed for further clarification - but their answer baffled me:
> The Slack instance you are asking about is a communication tool used by the WordPress volunteer community to coordinate on the project to build and maintain the open source WordPress software. **There is no business or data controller that owns or manages this Slack.** If one or more of the volunteers had a private discussion about you in this Slack you would need to direct your request to those individuals and they would need to decide themselves how to handle your request.
>
>
(Emphasis added.)
This, to me, implies that they are not following [Slack's term's and conditions](https://slack.com/intl/en-gb/terms-of-service/user) which explicitly say the owner of the Slack has to comply with data requests.
> As between [Slack] and the customer, you agree that it is solely the customer’s responsibility to […] respond to and resolve any dispute with you and any authorised user relating to or based on customer data
>
>
Is this Slack *really* owned by volunteers? According to <https://wordpress.slack.com/account/workspace-settings#admins> - the *primary* owner is WordPress.org itself. Although there are several other users listed as owners, including Matt himself.

I specifically asked WordPress.org for details of their GDPR registration. Their reply is hilarious:
> WordPress.org is privately owned by a person, not by a registered or covered entity.
>
> While the email address says “Data Protection Officer” this is merely to make it easy for Europeans to find and contact the privacy volunteers who, of course, want to do their best to assist persons with privacy related questions and requests. This does not indicate that WordPress.org is a GDPR covered website or owned by any entity which is subject to the GDPR.
>
>
So now we're at an impasse. I have no way of knowing if the anonymous tip-off I received was genuine and I can't prove if WordPress are concealing messages to me. I think it is fair to say that [other people feel that WordPress.org doesn't really understand the GDPR](https://wpandlegalstuff.com/the-not-affiliated-checkbox-and-the-gdpr/) - so we can add this example to the list.
To sum up:
* The website processes millions of users' data, yet has no GDPR policy.
* Volunteers are apparently cosplaying as Data Protection Officers, without any real knowledge of how GDPR works.
* An [official WordPress.org Slack](https://make.wordpress.org/chat/) is run by WordPress.org with Matt & others as admins.
* This Slack processes the data of over 50,000 users *without* any GDPR compliance.
In my opinion, this is no way to run a major piece of web infrastructure. The community deserves better., Is WordPress.org GDPR Compliant?, Terence Eden’s Blog, 01jev01fph7gcp7tac6s4y1v8j.