Kaspars Dambis’ Post
## Metadata
- Author: [[Kaspars Dambis]]
- Full Title: Kaspars Dambis’ Post
- Category: #articles
- Document Tags: [[acf]] [[wpdrama]]
- Summary: The ACF vulnerability that is "fixed" by the Secure Custom Fields plugin is not an actual vulnerability. The updated code path gets executed only if:
1…
- URL: https://www.linkedin.com/posts/kaspars-dambis_the-acf-vulnerability-that-is-fixed-by-activity-7251522994483720192-b_ro?utm_source=share&utm_medium=member_ios
[Kaspars Dambis](https://lv.linkedin.com/in/kaspars-dambis?trk=public_post_feed-actor-name)
Full-stack web developer and team leader with passion for WordPress, teaching and sustainable living.
The ACF vulnerability that is "fixed" by the Secure Custom Fields plugin is not an actual vulnerability. The updated code path gets executed only if:
1. You're using ACF to define custom post types or taxonomies,
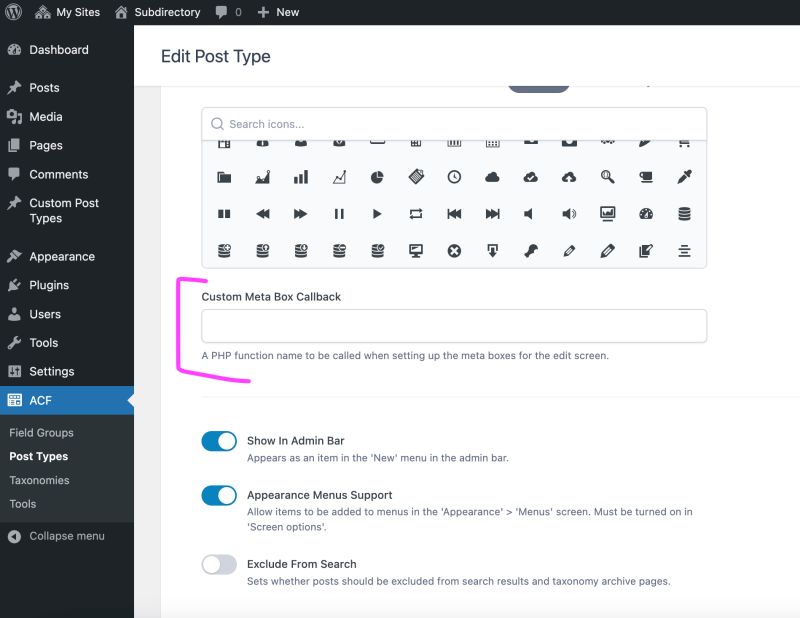
2. AND an administrator-level user has specified a custom metabox callback function that (a) already exist in your codebase and (b) is somehow malicious.
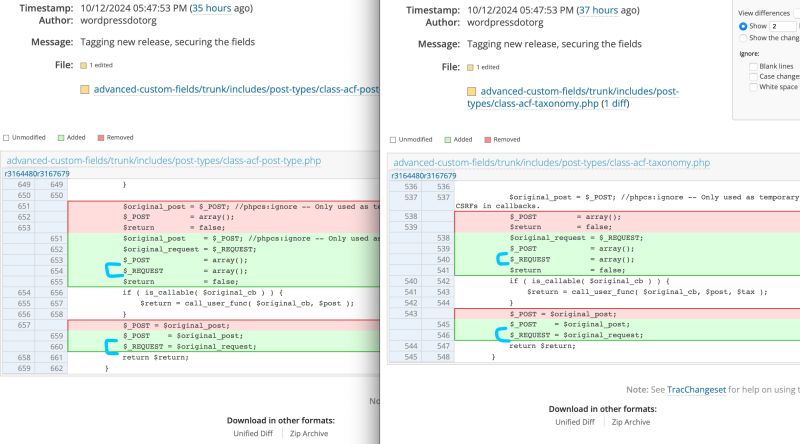
The patch applied to SCF simply clears out the $\_REQUEST global variable that would be available to any such callback function like it already did with $\_POST variable before the change.
* 
* , Kaspars Dambis’ Post, Kaspars Dambis, 01jah7vy5jhyrjzxwqw5bvq9nv.