PBOM vs SBOM: A New Security Standard
## Metadata
- Author: [[Yael Citro]]
- Full Title: PBOM vs SBOM: A New Security Standard
- Category: #articles
- Document Note: ---
tags: [#pbom, #sbom, #software-supply-chain, #application-security]
- #pbom
- #sbom
- #software-supply-chain
Author: Yael Citro, OX Security
Source: OX Security Blog
Reference: [PBOM vs SBOM: A New Security Standard](https://www.ox.security/pbom-vs-sbom/)
date created: 2025-05-16 20:15
---
# Title: 🔄 PBOM vs SBOM: A New Security Standard
## Table of Contents:
- [📝 Summary](#📝-summary)
- [📖 Main Content](#📖-main-content)
- [🗒️ Notes](#🗒️-notes)
- [📖 References](#📖-references)
- [🗣️ Paraphrase](#🗣️-paraphrase)
- [📰 Newsletter](#📰-newsletter)
- [✅ Action Items](#✅-action-items)
- [🧪 Hypotheses](#🧪-hypotheses)
- [📊 Methodology](#📊-methodology)
- [❓ Questions](#❓-questions)
- [🔮 Future Research](#🔮-future-research)
- [💡 Implications](#💡-implications)
- [🧠 Learning Styles Assessment](#🧠-learning-styles-assessment)
- [📊 Accessibility Assessment](#📊-accessibility-assessment)
- [🌍 DEIB Assessment](#🌍-deib-assessment)
- [✅ Logical validity](#✅-logical-validity)
- [🔍 DARVO Analysis](#🔍-darvo-analysis)
- [🔍 SEO Evaluation](#🔍-seo-evaluation)
- [🎯 Conclusion](#🎯-conclusion)
---
## 📝 Summary:
The article explores the limitations of the traditional Software Bill of Materials (SBOM) as a supply chain security tool and introduces the Pipeline Bill of Materials (PBOM) as a more comprehensive and proactive solution. PBOM not only tracks what’s in a software artifact but also traces how and where it was built, ensuring full traceability and integrity at every build stage. By shifting the focus from “what is inside” to “how it was made,” PBOM offers a next-generation approach to secure software supply chains.
---
## 📖 Main Content:
The rapid growth of software supply chain attacks has exposed weaknesses in how organizations track and secure the components that make up their applications. The SBOM, while an essential first step, is limited because it only inventories components present in the final product. It does not provide visibility into the processes, tools, or environmental context involved in the build pipeline, nor does it guarantee that the SBOM itself hasn’t been tampered with.
OX Security’s PBOM approach seeks to address these gaps by including the entire build pipeline’s metadata—source code, dependencies, build tools, environment variables, pipeline run logs, and more. The PBOM is designed to be cryptographically sealed at every stage, enabling validation of the complete lineage of a software artifact from code commit to deployment.
Key innovations in PBOM include:
- Automated evidence gathering and chain-of-custody tracking at every build step.
- Use of cryptographic signatures to guarantee data integrity and authenticity.
- Continuous, real-time monitoring and alerts for unauthorized changes or risky behaviors during the build process.
- Support for compliance and regulatory requirements by providing auditable records of every build activity.
OX Security argues that PBOM will become essential as the threat landscape evolves, particularly with increasing regulatory scrutiny on software provenance and the growing sophistication of supply chain attacks.
### 🗒️ Notes
- **SBOM (Software Bill of Materials):**
- Lists software components and dependencies.
- Required by many modern compliance standards.
- Lacks visibility into the software build process.
- Can be falsified or outdated, providing a false sense of security.
- **Supply Chain Attacks:**
- Exploit weaknesses in the development and build process.
- Notable cases: SolarWinds, Codecov, and more.
- Attackers often target CI/CD pipelines, not just software dependencies.
- **PBOM (Pipeline Bill of Materials):**
- Tracks every step in the build pipeline.
- Includes provenance data—who, what, where, when, and how.
- Uses cryptographic sealing at each stage to prevent tampering.
- Provides real-time alerts and auditing capabilities.
- Bridges gaps left by SBOM, covering everything from initial source to deployment.
- **Regulatory & Compliance Impact:**
- PBOM supports compliance with emerging government and industry regulations.
- Enables full forensic investigation in case of breaches or compliance checks.
- **OX Security’s Position:**
- PBOM is a logical next step for supply chain security.
- Advocates for industry adoption to counter increasingly advanced threats.
---
## 📖 References:
- [PBOM vs SBOM: A New Security Standard – OX Security](https://www.ox.security/pbom-vs-sbom/)
- [CISA: Securing the Software Supply Chain](https://www.cisa.gov/resources-tools/resources/securing-software-supply-chain)
- [NIST SP 800-218: Secure Software Development Framework](https://csrc.nist.gov/publications/detail/sp/800-218/final)
- [SolarWinds Attack Analysis (Cybersecurity & Infrastructure Security Agency)](https://www.cisa.gov/news-events/news/alert-aa21-008a)
---
## 🗣️ Paraphrase:
1. **Original:**
“SBOMs have played a crucial role in helping organizations identify what’s inside their software. But as supply chain attacks become more advanced, it’s clear that knowing only what is inside is no longer enough.”
**Paraphrased:**
SBOMs help organizations understand the components within their software, but given the increasing complexity of attacks, simply knowing the ingredients isn’t sufficient to ensure security.
2. **Original:**
“PBOM technology provides a list of software’s lineage and ensures the security and integrity of every build.”
**Paraphrased:**
PBOM tracks the full history of how software was created, guaranteeing its integrity and the authenticity of every build step.
---
## 📰 Newsletter:
🚨 **Supply Chain Security: Beyond SBOM!**
If you thought keeping a software ingredients list (SBOM) was enough, think again! OX Security introduces PBOM—Pipeline Bill of Materials—as the new gold standard for supply chain integrity. PBOM not only catalogs what’s in your code, but also traces how, where, and by whom it was built, using cryptographic seals and real-time monitoring.
Whether you’re maintaining WordPress plugins or running enterprise CI/CD pipelines, supply chain security is no longer “set and forget.” Dive into the full PBOM vs SBOM breakdown [here](https://www.ox.security/pbom-vs-sbom/) and see how your process stacks up!
---
## ✅ Action Items:
- **Educators and Advocates:**
- Teach contributors and teams the difference between SBOM and PBOM and why provenance matters.
- Incorporate PBOM concepts into onboarding and contributor documentation, emphasizing secure build practices.
- Host workshops or brown-bags on CI/CD pipeline security, leveraging PBOM as a practical framework.
- Evaluate open-source tools for PBOM generation and integration in WordPress development workflows.
- Advocate for cryptographic build provenance standards within OSPOs and community projects.
- **Alignment with Professional Focus:**
- PBOM represents an actionable, transparent approach to software supply chain security—crucial for building trust in open source.
- By championing PBOM adoption, you position yourself and your organization at the forefront of regulatory compliance and contributor security education.
- The article aligns with advancing transparency, sustainability, and proactive risk management in the open-source ecosystem—key goals for OSPO leadership.
---
## 🧪 Hypotheses:
- H1: Integrating PBOMs in open source projects will reduce the frequency and impact of supply chain attacks compared to SBOM-only approaches.
- H2: PBOMs improve developer accountability and traceability in collaborative, distributed development environments.
- H3: Regulatory adoption of PBOM requirements will drive industry-wide improvement in supply chain transparency.
### 📊 Methodology:
- Compare incident rates in projects using PBOM vs SBOM across diverse OSS ecosystems.
- Survey contributors and maintainers about perceived ease and value of PBOMs.
- Conduct compliance audits of PBOM-enabled and SBOM-only pipelines.
- Pilot PBOM integrations in various CI/CD systems; track time-to-detection and response for simulated attacks.
### ❓ Questions:
- What are the technical barriers to implementing PBOM in smaller OSS projects
- Summary: SBOM does not go far enough. OX Security's PBOM technology provides a list of software's lineage and ensures the security and integrity of every build.
- URL: https://www.ox.security/pbom-vs-sbom/?utm_campaign=GT-DSA&utm_medium=cpc&utm_source=google&utm_content=&gad_source=1&gclid=Cj0KCQjwytS-BhCKARIsAMGJyzrOy2rwjoUKYwXWsxqHJydHdhJ7QQIVegQf6k0PW_LG5fBAVApRBP8aAmlHEALw_wcB


#### What is an SBOM?
The traditional concept of Software Bill of Materials (SBOM) is familiar to development stakeholders just as a Bill of Materials (BOM) is familiar to any manufacturer.
For decades, manufacturers have been using a BOM to document complex manufactured goods down to their smallest components. This allows them to track the origin and status of each component in any given product. As a result, an engine manufacturer knows exactly which engines of the hundreds of thousands produced contain a flawed part. And which cars need to be recalled to rectify that flaw.
Similarly, developers use an SBOM to list the name, version, license, and any vulnerabilities of their open-source components, as well as the components in those components used to develop and build a piece of software. The SBOM is important for quality control and [crucial for software supply chain security](https://www.ox.security/software-supply-chain-security-and-sbom/).
#### Software supply chain security is top of mind
[Software supply chain security, like cybersecurity as a whole, is top of mind for most DevOps teams](https://www.businesswire.com/news/home/20220803005760/en/Black-Hat-USA-Research-Supply-Chain-and-Cloud-Security-Risks-Are-Top-of-Mind). Gartner predicts that by 2025, 45% of organizations worldwide will have experienced attacks on their software supply chains. And these attacks are increasingly sophisticated and difficult to detect. In order to counter this threat, software suppliers need to understand exactly what’s included in their code. They need to be able to identify the source of a vulnerability F-A-S-T in order to remediate it before the entire supply chain is threatened.
#### SBOMs are not enough
The problem is, an SBOM doesn’t actually cover the entire software supply chain. SBOMs are only static lists of mapped open-source software dependencies. These lists simply do not go far enough to provide the end-to-end security and integrity a dev pipeline needs. SBOMs only scan part of the software supply chain. As a result, despite the best efforts of SBOM providers, today’s software supply chains remain a black box. And the most pressing challenge in software supply chain security is how to turn that black box into a source of security and business intelligence.
That’s why we created PBOM (Pipeline Bill of Materials) standard.
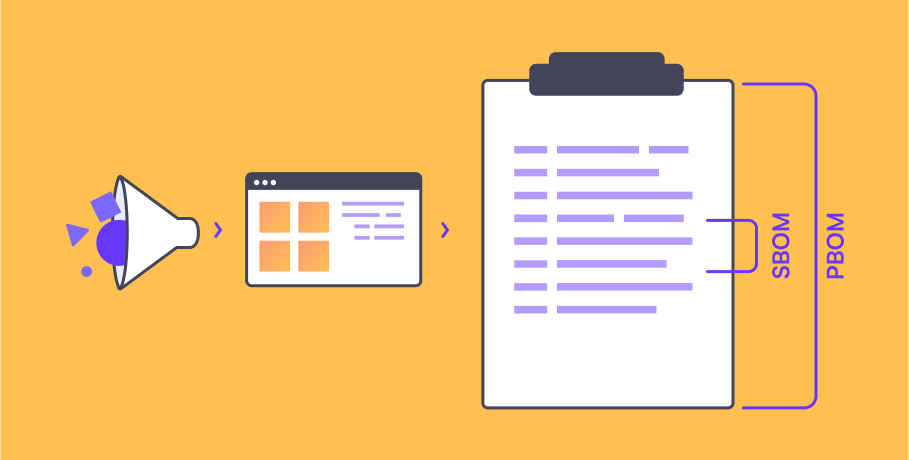
#### What is Exploitable vs. Not-Exploitable How to Tell the Difference for Your Software Vulnerabilities. [Read more](https://www.ox.security/exploitable-vs-not-exploitable-can-you-tell-the-difference-for-your-software-vulnerabilities/) a PBOM? Ox Security’s [PBOM](https://www.ox.security/the-anatomy-of-a-pbom/) standard provides a real-time list of software lineage, from the first line of code all the way to release while identifying and preventing threats along the way. PBOM ensures the integrity of every build, verifies that all apps in production are secure, and minimizes the attack surface. More than just an SBOM-like inventory of components in your production apps, a [PBOM](https://www.ox.security/the-anatomy-of-a-pbom/) is a dynamic list of everything a piece of software has gone through. It starts with the first line of code and continues all the way through to release, identifying any vulnerabilities along the way. Light-years beyond an SBOM, a PBOM is a signed ledger of each pipeline build. A PBOM tracks the entire software life cycle, including all version lineage, SLSA.dev, SaasBOM, security tool results, build hashes, and more.
#### What can PBOM do for me?
PBOM maximizes software supply chain security and integrity with an automated process that covers all software, from the first line of code, delivering:
* **Complete pipeline security** – PBOM standard automatically tracks all pipeline branches, builds, pull requests, tickets, known issues, and vulnerability management. This enables full visibility into your organization’s security posture.
* **Comprehensive integrity** – PBOM ensures that software is built from the correct sources and dependencies and hasn’t been modified during the build process. It verifies no “bad” code is submitted without alert and review. It also verifies no malicious code is pushed via a compromised pipeline.
* **Full traceability** – PBOM continuously monitors every pipeline change – from proper documentation of changes to tracing each of your software releases.
PBOM enables dev stakeholders to verify that each version or artifact provided to external customers has been checked properly and that the release is “worthy”. It empowers dev teams to compare artifacts in production to the PBOM ledger to ensure tractability on each release. And it helps dev teams gain visibility into each pipeline in the internal build environment – marking each artifact with a proper security tag.
#### The Bottom Line
The software industry’s long reliance on SBOMs has left large parts of the software supply chain attack surface in the dark. Now, PBOM offers a new standard for software supply chain security. It provides DevOps teams with full visibility over the software supply chain attack surface. This includes source code, pipeline, artifacts, container images, runtime assets, and applications. It also continuously monitors security changes in the environment. This ensures that the software supply chain does not drift from its original secure state. What’s more, PBOM delivers clear and actionable remediation strategies. This includes a list of prioritized risks and recommendations based on context and company business objectives.
And in a development ecosystem that demands both speed and security, PBOM minimizes the attack surface without impeding developer agility. This prevents software supply chain attacks without slowing down development.
Want to learn more? [Book a demo](https://www.ox.security/book-a-demo/) today., PBOM vs SBOM: A New Security Standard, Yael Citro, 01jpcs2zs5y8hj7cyqeaf0hast.